
Secret keys in your code
Stripe, AWS, OpenAI and other keys that ended up in code anyone can download from your site.
Monthly security scans for apps that keep changing. A person checks every finding.
$299/month. 4-month minimum, then month-to-month.

A new feature, a new tool or a new host can expose something you didn't mean to. A monthly scan finds it before someone else does.
A Stripe secret key slips into a JavaScript bundle anyone can download.
The next monthly scan flags it. You move it server-side and roll the key.
A new database table goes live without access rules.
The scan finds it readable without logging in. A one-line policy fixes it.
The old login page is still online, with no rate limit.
The scan finds the forgotten page before anyone else does.
45%
of AI-generated code samples had a security flaw when 100+ AI models were tested on 80 coding tasks.
Veracode, 2025 GenAI Code Security Report (opens in new tab)37.6%
more critical security holes after just five rounds of asking an AI to improve the same code.
Shukla, Joshi & Syed, 2025 (arXiv 2506.11022) (opens in new tab)170
of 1,645 apps built on one popular AI app builder had databases anyone could read.
Matt Palmer, statement on CVE-2025-48757 (opens in new tab)$56,600
average cost of a reported cyber attack on an Australian small business last year.
ASD Annual Cyber Threat Report 2024-25 (opens in new tab)We test your live app from the outside, the way an attacker would. We don't change anything, and we don't start until you've signed.
Stripe, AWS, OpenAI and other keys that ended up in code anyone can download from your site.
Supabase tables with no access rules, open Firebase databases and file storage.
Old staging sites and test apps that are still online.
Outdated software and plugins with published flaws (CVEs).
.env and .git files, backups, admin logins and default passwords.
Old protocols, weak encryption and certificates about to expire.
Whether anyone can send email as you (SPF, DMARC and DKIM).
Core, plugins and themes with known holes.
Pick a plan, list up to 3 sites or apps and pay with Stripe. It takes about two minutes.
Your service agreement and your permission to test, both inside your portal. We test nothing until you sign.
Your full deep scan starts. Results land in your dashboard, usually within 5 business days.
Tell us when you have fixed something and we re-test it for free. Every month we check everything again.
The few issues worth fixing first, what each one means, and the steps to fix it.
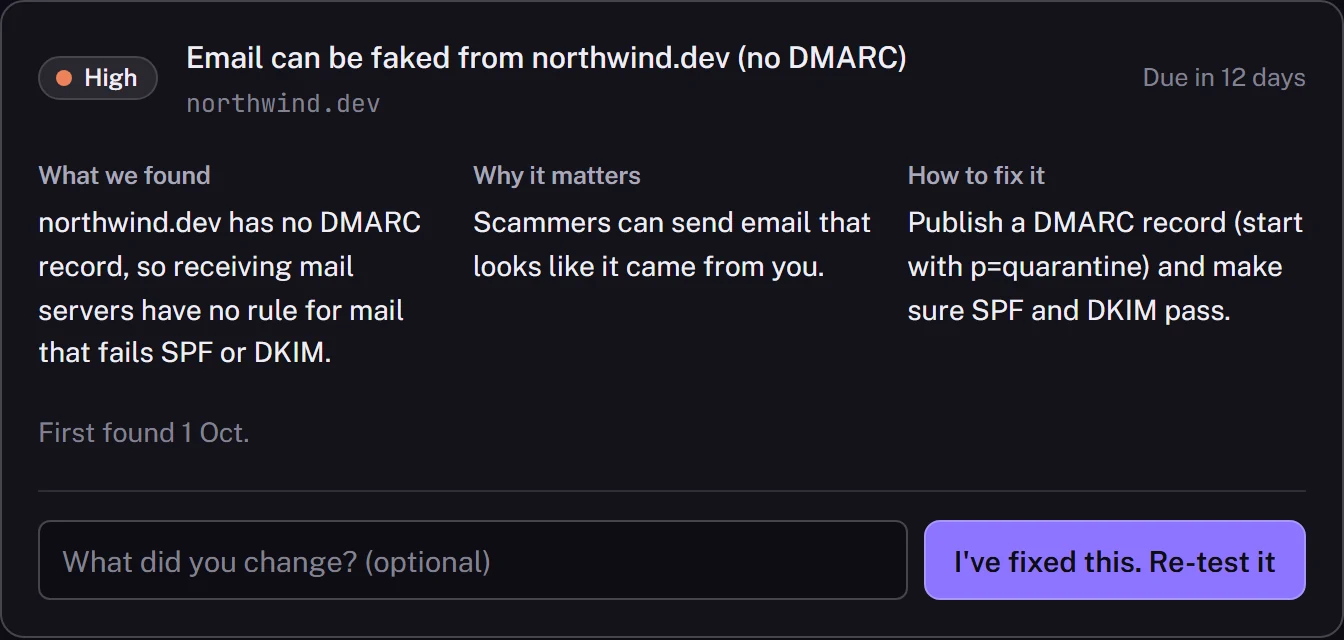
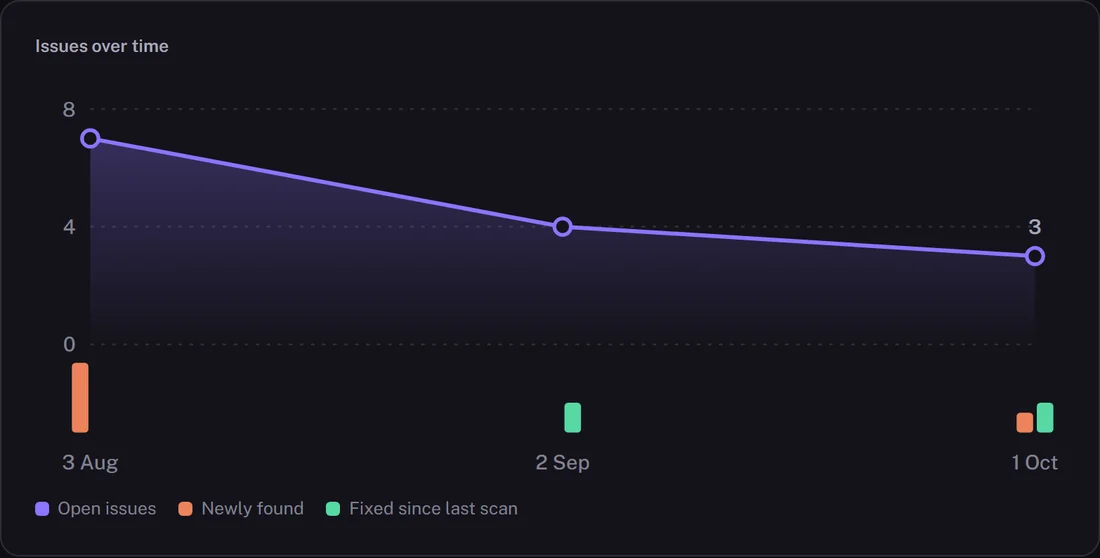
Real dashboard, sample data.
Pay online in a couple of minutes. Your login arrives by email straight away.
Your full deep scan in month 1, then we check everything again every month.
$299 / month
That's the total: no GST is added. 4-month minimum, then month-to-month.
Start monthly scansOne full, hands-on check of your app, with a written report. Good for a launch, a funding round or a customer's security questionnaire.
$3,500 once
That's the total: no GST is added.
Get a deep scan4 months of Monthly Scans costs $1,196 and includes the same deep scan, plus 3 more monthly scans.
Need a deeper look at your company's IT too? We also run a Cyber Health Check against the Australian Government's Essential Eight, and a Microsoft 365 & Google Workspace check.
No. We test your live app from the outside, the way an attacker would. You tell us which sites and apps to check.
No. Our checks only read. We don't change data, crash servers or log in as your users, and our scanner identifies itself in your logs.
Yes, and it's why the scan runs every month. Each scan checks what's live that day, and you can ask for an extra re-scan after a big release.
Your first month includes the full deep scan, which costs $3,500 on its own. The minimum of 4 monthly payments ($1,196 in total) covers that. After that it's month-to-month.
Before anything reaches your dashboard, we confirm it's real, rate how serious it is for your app, and write the fix in plain English.
No. We tell you the exact changes to make, step by step, so you can hand them to your developer or paste them into your AI coding tool. Most fixes are a setting or a few lines of code.
$299/month, 4-month minimum. We test nothing until you sign. Terms